4 WordPress Maintenance Tasks That Need a Backup Owner
A WordPress site can look well maintained right up until the one person who knows how it works is unavailable. A staff departure, extended absence, unresponsive freelancer, or agency transition can quickly expose gaps in login access, billing ownership, update approvals, backup recovery, and incident response. The technical problem may be small; the disruption often comes from nobody else having the authority or information to act.
For Canadian businesses, WordPress maintenance ownership is not about giving every employee full control of the website. It is about ensuring that routine work and urgent decisions can continue through an authorized backup person or a documented support process. The goal is practical continuity: the business retains control of its accounts, knows who can approve changes, and can reach the right people when something needs attention.
WPAssist commonly sees this risk in otherwise capable organizations. The site may have been built by a trusted specialist, but the ownership details were never formalized as the business grew. A short review now is usually far easier than trying to reconstruct access and responsibilities during an outage, campaign launch, or renewal deadline.
Quick Answer
Four WordPress maintenance responsibilities should never rely on one person alone: administrative access, update approval and deployment, domain and licence renewals, and monitoring-alert response. Assign a primary owner and an authorized backup for each, keep business-controlled credentials and billing records current, and document the steps another person needs to take. Shared accountability reduces delays without requiring everyone to be a WordPress administrator.
Key Takeaways
- Business-controlled access matters more than one person’s familiarity with the site.
- Updates need a clear approval path, a safe deployment process, and a fallback plan.
- Domains, licences, and renewal notices need named owners and backup contacts.
- Alerts are useful only when more than one authorized person can receive and act on them.
- A concise handoff record turns routine maintenance into a repeatable business process.
Why single-person maintenance dependencies create business risk
A single-person dependency exists when one employee, contractor, freelancer, or agency contact is the only person who can complete a necessary website task. That person may hold the only administrator login, receive all renewal notices, approve all changes, or know where the backup and hosting accounts are located. The risk is not a reflection on that individual. It is a process weakness that becomes visible when availability changes.
Routine WordPress work spans several systems, not just the dashboard. Your domain registrar, DNS provider, hosting account, WordPress users, premium theme and plugin licences, backup storage, email addresses for notices, and monitoring tools may all have separate credentials. If these accounts are registered to a personal email address or protected by one person’s authentication device, the organization can lose time precisely when it needs to move quickly.
Continuity does not mean unlimited access. It means the business has at least two authorized routes to perform essential work, with permissions matched to each person’s role. A marketing lead may need authority to approve content and campaign changes; a technical support partner may need access to implement and validate them; an executive or operations lead may retain control of billing and account recovery.
This article focuses on ownership and continuity. The financial comparison between ongoing coverage and reactive repair is a related but different question; the cost of waiting for an emergency can change the value of ongoing WordPress support, while a continuity review asks whether someone can act at all when the usual contact is unavailable.
1. Administrative access and account recovery
The first task to review is control of the site itself. WordPress user accounts can be assigned roles with different capabilities, and an administrator has access to all administration features within a single site. Review administrator site access with the same care you would apply to a business bank login or a critical software account.
Start by identifying every person and organization with administrator-level access. Then ask a more important question: if the primary administrator could not respond today, who could legitimately reset credentials, update a user, disable a compromised account, or restore access without starting a lengthy recovery process?
Keep ownership with the business
Whenever possible, core accounts should use a business-controlled email address rather than an individual’s personal inbox. The organization should be able to receive password-reset messages and renewal notices even after staffing changes. Store credentials in an approved password manager, not in an unprotected document, email thread, or browser profile belonging to one person.
That does not require a shared WordPress login. Individual accounts create a clearer record of who made changes and make it easier to remove access when responsibilities change. Give each authorized person only the access they need, and review accounts after employee departures, agency changes, or major role shifts.
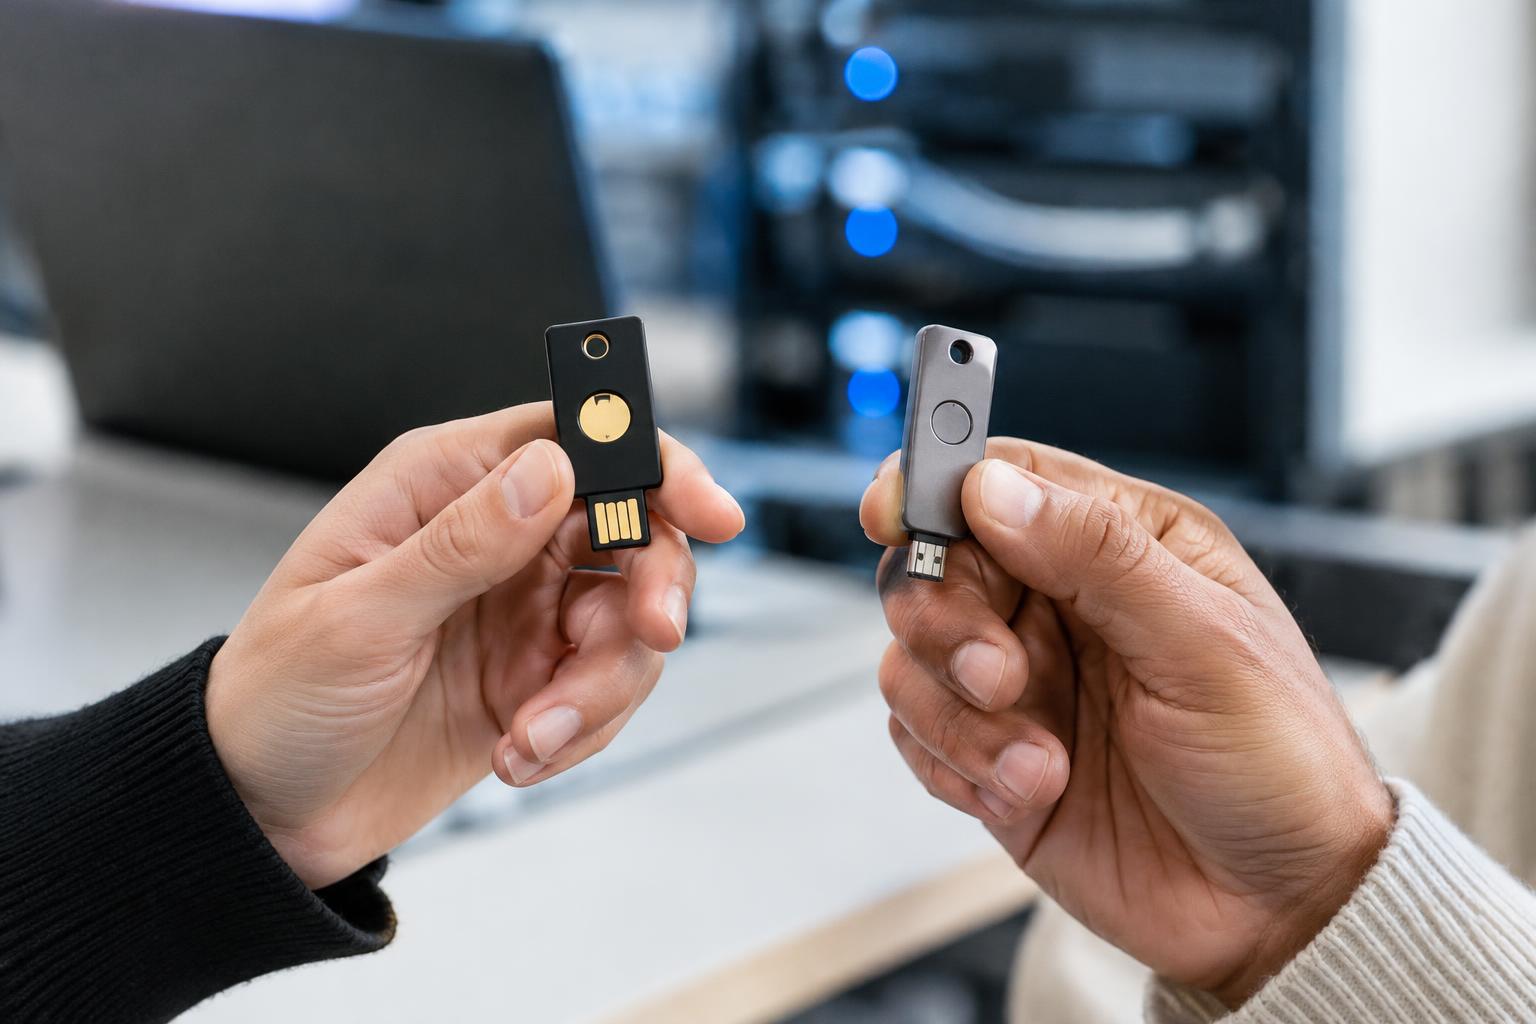
Also map the recovery path. If multi-factor authentication is enabled, identify who controls the recovery method and where emergency recovery information is held. If a hosting account or domain registrar requires identity verification, make sure the business contact details are current. A login list without account-recovery ownership is incomplete.
What to look for: a warning sign is hearing “only our developer knows that password.” Proof of a serious continuity issue is discovering that the business cannot access the email account, authentication method, or billing profile needed to recover the developer’s account. Treat the first statement as a cue to investigate, not as a reason to assume the worst.
2. Update approvals and safe deployment
Managed WordPress updates should not depend on one person’s memory or personal judgement. Core, plugin, theme, PHP, and configuration changes can affect forms, ecommerce functions, display layouts, tracking, membership access, and integrations. Someone needs to determine what can proceed routinely, what requires business approval, and what to do if a change causes an issue.
The central principle is simple: separate approval from implementation where practical, and make both steps visible. In software delivery more broadly, approval before production is a recognized control point; AWS describes manual approval before changes are promoted to production in a continuous-delivery workflow. The same principle transfers well to WordPress, even though a small business site will not necessarily use a formal development pipeline.
Define what needs approval
Not every update deserves a meeting. A documented process can distinguish low-risk routine work from changes that affect customer experience or revenue. For example, a security update may follow a pre-approved maintenance process, while a WooCommerce payment extension update might require a planned window and checkout testing. A homepage redesign, new analytics configuration, or plugin replacement should usually have a clear business approver.
Imagine a retailer preparing for a weekend promotion. A contractor who usually performs updates is travelling, and a payment-plugin update becomes available on Friday afternoon. A workable process tells the backup contact whether to proceed, defer, test in a staging environment if one exists, check a defined set of customer paths after deployment, and escalate if checkout behaviour changes. Without that process, the team either delays a necessary update or makes a rushed decision without context.
At WPAssist, we encourage clients to treat update history, validation steps, and rollback options as shared operational information rather than private technical knowledge. The person who approves a change should know its purpose and timing; the person who performs it should know the boundaries of the approval and what success looks like afterward.
A safe update workflow does not promise that conflicts will never happen. It gives another authorized person enough context to make a controlled decision, communicate with stakeholders, and reverse course when a post-update check identifies a problem.
3. Domain, hosting, and licence renewals
A site can be technically healthy and still become unavailable because a registration or subscription was missed. Domain renewal is especially important because the domain connects visitors and email users to services the business depends on. ICANN advises registrants to renew before expiration if they want to keep using a domain name and associated services.
Licence renewals deserve similar attention, although their consequences vary. An expired premium plugin or theme licence may not immediately break a site, but it can end access to updates, support, or features. Hosting, SSL certificates, backup storage, transactional email, security services, and third-party integrations can each have their own billing dates and notices.
The issue is rarely that one person is incapable of renewing an account. The issue is that the account may be registered under that person’s name, billed to their card, and connected to an inbox nobody else monitors. When they leave, the business may not know the provider, renewal date, credentials, or even whether auto-renewal is active.
Build a renewal register that someone can use
Keep a concise register for essential accounts. It should record the service, account owner, billing contact, renewal date or renewal setting, payment method owner, login location, and primary and backup responsible people. Do not place passwords in the register; point authorized users to the approved password manager instead.
For a typical Canadian business, the minimum list often includes the domain registrar, DNS provider, host, WordPress administrator accounts, backup provider, premium plugin and theme licences, email delivery service, and any ecommerce or booking integrations. Review it quarterly and whenever the business changes staff, agencies, payment cards, or legal entity details.
Use a shared mailbox or distribution list for renewal notices where appropriate. That reduces the chance that a deadline disappears into one person’s inbox. It also gives finance and technical contacts a chance to confirm whether a charge is expected before a renewal becomes urgent.
4. Monitoring alerts and the first response
Monitoring only helps if the alert reaches someone who can interpret it and take the next step. Uptime alerts, security notices, backup failures, expiring certificates, unusual resource usage, and critical plugin notifications should not route to one personal email address or a single unattended inbox.
Assign a primary recipient and at least one backup recipient for each alert category. Then define the expected response: acknowledge, check whether the issue is customer-facing, capture relevant details, attempt an approved first action if applicable, and escalate to the technical owner or support provider. An alert without a response path is information, not operational coverage.
Be realistic about roles. A business owner does not need to troubleshoot a database error at midnight, but they should know who receives the alert and how to authorize work if the site is down. A marketing manager does not need hosting credentials if a technical partner has them, but the manager may need a way to report a broken landing page and confirm whether a campaign should be paused.
Consider a simple scenario: an uptime monitor reports that a lead-generation site is unavailable early on a weekday. The backup recipient checks whether the problem is isolated or persistent, confirms whether forms and key pages are affected, and contacts the designated technical responder using a pre-agreed channel. The business contact receives a plain-language status update. This is a better outcome than an alert sitting unread until the usual site owner returns from vacation.
Monitoring coverage should include communications coverage. Make sure the team knows who can speak to the hosting provider, who can approve emergency work, and who needs to be informed when an incident affects customers, campaigns, or revenue.
How do you document a WordPress maintenance handoff?
A handoff document does not need to be a long technical manual. It needs to let an authorized person orient themselves quickly, locate the right systems, understand normal responsibilities, and escalate unusual issues. Keep it current, stored in a business-controlled location, and accessible to the people who genuinely need it.
Documentation turns individual know-how into a repeatable process. The best handoff records explain both the “where” and the “what”: where accounts are controlled, what routine work occurs, who approves changes, and what should happen when a routine task cannot proceed normally.
A compact continuity checklist
- List the business owner and backup owner for WordPress, hosting, domain, DNS, backups, licences, and monitoring.
- Confirm that two authorized people can access account recovery methods without sharing a single login.
- Record the update process, including approvals, testing expectations, validation checks, and escalation contacts.
- Track renewal dates, billing contacts, and where notices are delivered.
- Define which alerts require immediate action and who responds when the primary contact is unavailable.
- Review the record after staffing changes, provider changes, major launches, or an incident.
For maintenance work performed by an external provider, ask for regular reporting that makes responsibilities visible. A useful report should show completed maintenance, notable findings, unresolved items, and follow-up ownership. Knowing what a maintenance report should cover helps a business distinguish meaningful oversight from a vague assurance that everything is handled.
Keep sensitive details proportionate. The handoff document can identify the password manager record or secure vault location rather than exposing passwords, recovery codes, or private keys in a broadly accessible file. Access should be reviewed, removed when no longer needed, and tested occasionally through a planned continuity check rather than an actual emergency.
When should you review maintenance ownership?
Review ownership before a problem forces the conversation. The best times are during onboarding with a new developer or agency, before a major campaign or seasonal sales period, after a leadership or staffing change, before renewing a key vendor, and when a business acquires or redesigns a site. A brief review is also worthwhile when the person handling WordPress says they are “the only one who knows how it works.”
Do not wait for perfect documentation. Start with the four areas in this article and close the biggest gaps first. If the business cannot recover the domain or hosting account, solve that before refining a detailed update checklist. If alerts go only to a departed employee, reroute them before trying to optimize notification rules.
There is also a useful distinction between named ownership and shared responsibility. Every task needs a named primary person so it does not become everybody’s vague job. Every critical task also needs a backup path so it does not become one person’s private responsibility. The two ideas work together.
A support arrangement can provide valuable coverage, but it should not remove the business from ownership of core accounts and decisions. The business remains responsible for knowing who is authorized, where critical services are held, and how to reach support when circumstances change. A capable provider makes that information clearer, not more obscure.
Conclusion
Single-person dependency is one of the quieter risks in WordPress maintenance because it can remain invisible while everything is running normally. By sharing authorized access, defining update approvals, tracking renewals, routing alerts to more than one person, and maintaining a short handoff record, your business can reduce avoidable disruption without overcomplicating day-to-day work.
The strongest maintenance process is not one where everyone has every password. It is one where the right people have the right level of access, routine work is documented, and the business can continue when a key person is unavailable. If you are reviewing whether your present coverage includes clear ownership and escalation, compare WPAssist’s WordPress maintenance pricing and support plans with the responsibilities your team needs covered.

Join Our Newsletter
Stay up to date on the latest WordPress tips and news